Automated VDR/VER reporting and a FedRAMP-compatible trust center, in one place.
Meet the FedRAMP 2026 vulnerability rules without spreadsheets. We turn your scan results into FedRAMP-ready reports and share them with agencies on demand, backed by the continuous monitoring team that has guided cloud providers through FedRAMP since 2011.
The FedRAMP 2026 deadlines are close.
The FedRAMP 2026 Consolidated Rules replace monthly scan spreadsheets with exposure-based vulnerability evaluation, machine-readable reporting, and trust center sharing.
December 7, 2026
Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) become mandatory for FedRAMP certified offerings.
January 1, 2027
The 2026 Consolidated Rules become mandatory for all FedRAMP stakeholders.
March 7, 2027
The VDR/VER grace period ends. Offerings that are not compliant risk losing certification.
Everything your continuous monitoring program needs for the 2026 rules.
Built on the same automation our team uses to deliver continuous monitoring
for FedRAMP customers today.

Automated vulnerability processing
- Import scans through connectors or a structured file upload
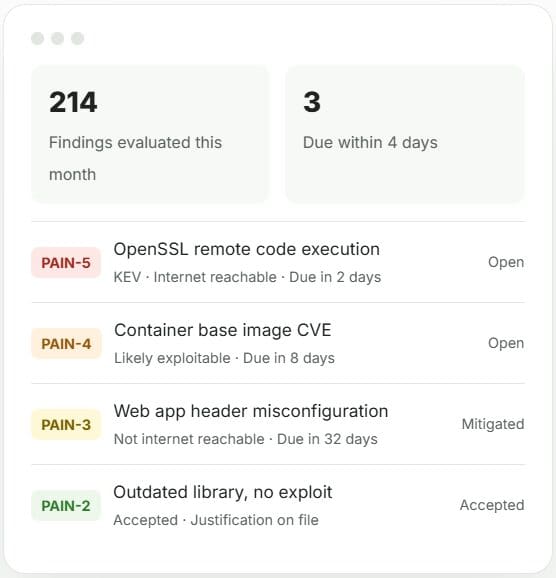
- Automatic CISA KEV and Vulnrichment lookups for every CVE
- Likely-exploitable and internet-reachability evaluation
- PAIN ratings and remediation due dates for your FedRAMP class

FedRAMP VER reporting
- Reports generated in the FedRAMP JSON schemas
- Human-readable monthly activity reports
- Accepted and historical vulnerability reporting
- Dated notes for accepted and overdue vulnerabilities

FedRAMP-compatible trust center
- On-demand access for agencies, assessors, and FedRAMP
- Documented APIs for programmatic access
- Agency access inventory and access logging
- Human- and machine-readable downloads

Inventory intake
- Upload the FedRAMP inventory template
- Or connect automated inventory sources
- Matches findings to assets and supports monthly verification

Incident and change reporting
- Guided forms for FedRAMP incident reports
- Significant change notifications
- JSON output published to your trust center
Coming 2027

Certification documents
- Security Decision Record (SDR), with SSP import
- Ongoing Certification Report (OCR) every quarter
- Certification Package Overview (CPO)
- Edit, review, and export at any time
From raw scans to agency-ready reports.

Connect
Load your inventory and connect your scanners, or upload scan exports. We handle onboarding with you.

Evaluate
Every finding is checked for exploitability, internet reachability, and KEV status, then rated and given a due date.

Report
FedRAMP JSON and human-readable reports are generated automatically, with your notes and justifications included.

Share
Agencies, assessors, and FedRAMP get on-demand access through your trust center, with every access logged.
Configured for your FedRAMP class.
Remediation timeframes and reporting requirements are applied for each system's certification class, so due dates match the rules you're held to.
A
Entry tier
A focused starting point for new FedRAMP offerings.
B
Low
Class B timeframes and reporting, without the overhead.
C
Moderate
Full VDR/VER automation for the most common certification class.
D
High
The strictest timeframes, tracked automatically.
Built to protect federal
certification data.
Your vulnerability data is sensitive. The trust center is designed around FedRAMP-style security controls.
Software built by the people who run continuous monitoring.
Landers and Company has guided cloud service providers through FedRAMP, DoD, GovRAMP, and CMMC since 2011. The trust center comes with that expertise: onboarding from our team, and optional hourly FedRAMP consulting whenever you need it.
2011
Supporting federal cloud providers
A–D
FedRAMP classes supported
U.S.
Hosting regions only
FAQ
Common questions
Get ready before December 7.
See the trust center in action and find out how quickly your systems can be onboarded.